Belkasoft X Forensic
Built for digital forensics experts, Belkasoft X Forensic helps you acquire, analyze, and report evidence from computers, mobile devices, cloud services, and more, all in one intuitive platform.
Belkasoft X Forensic
Belkasoft X is a versatile software tool for digital forensics and cyber incident investigations used worldwide by government agencies, law enforcement and private experts working for them.
Comprehensive investigations
Belkasoft X Forensic acquires, examines, analyzes, and presents digital evidence from various sources, including computers, mobile devices, RAM, cars, drones, and cloud services, in a forensically sound manner. Additionally, if you need to share case details with your colleagues, you can utilize a free-of-charge portable Evidence Reader.
Easy-to-use
Belkasoft X Forensic is user-friendly software that works out of the box and can be easily integrated into customer workflows. This allows users to start working with their cases immediately after the deployment of Belkasoft X Forensic.
Quick and smart
Belkasoft X Forensic employs efficient search techniques to swiftly locate the most forensically relevant artifacts, minimizing time spent on redundant operations during evidence collection. Powerful analytical features, including a connection graph, a timeline, and advanced picture and video analysis, facilitate rapid fact uncovering.
Save your time and efforts
Belkasoft X Forensic automates extraction and analysis tasks efficiently. This product can run unattended or be automated using the command line, enabling you to multitask and complete investigations more quickly.
Tailored to your needs
Whether you work as a digital forensic laboratory expert for a federal law enforcement agency or as an investigator at a local or state police department, our perpetual licensing and affordable pricing will perfectly suit your needs and budget.
Time-proven
Belkasoft has been developing the product for over 20 years, with feedback from investigators in law enforcement and business.
Digital Forensics Made Smarter
Belkasoft X Forensic combines advanced analysis with ease-of-use to help you solve cases faster and with precision.
Belkasoft X is an all-in-one tool
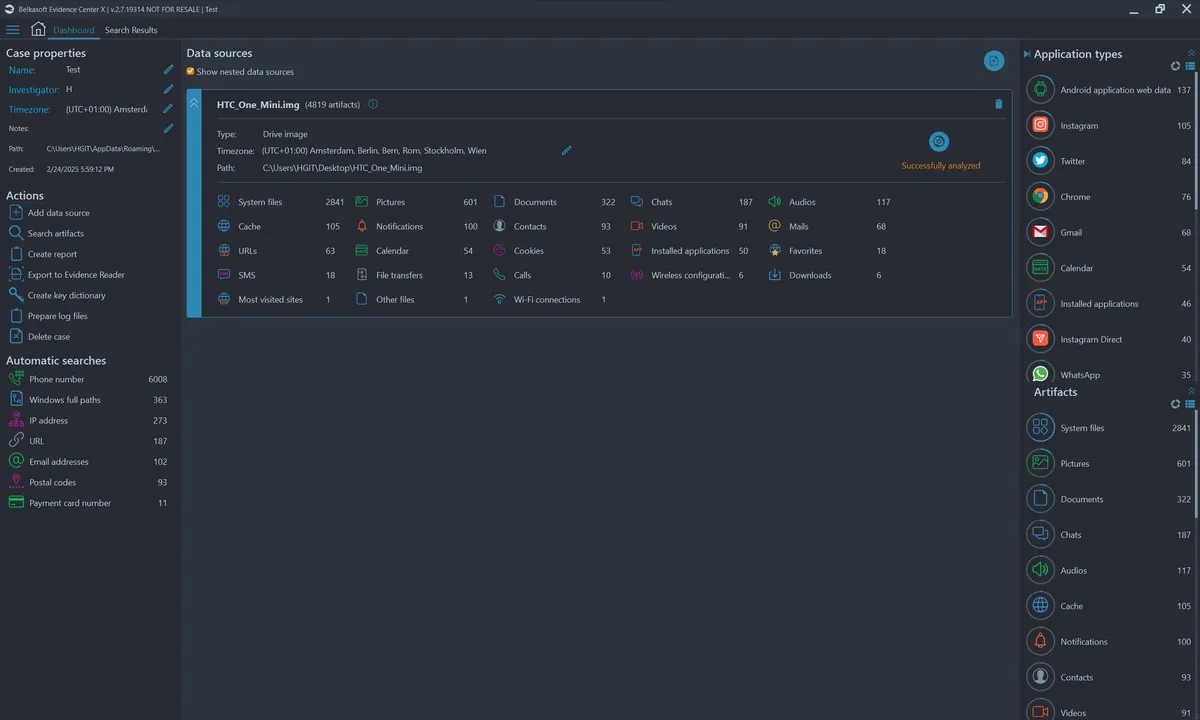
It allows you to analyze multiple data sources acquired from different electronic devices within one case.
Advanced Search and Analysis Tools
Belkasoft X provides a range of search and analytical tools that facilitate efficient data examination and streamline the identification of crucial evidence.
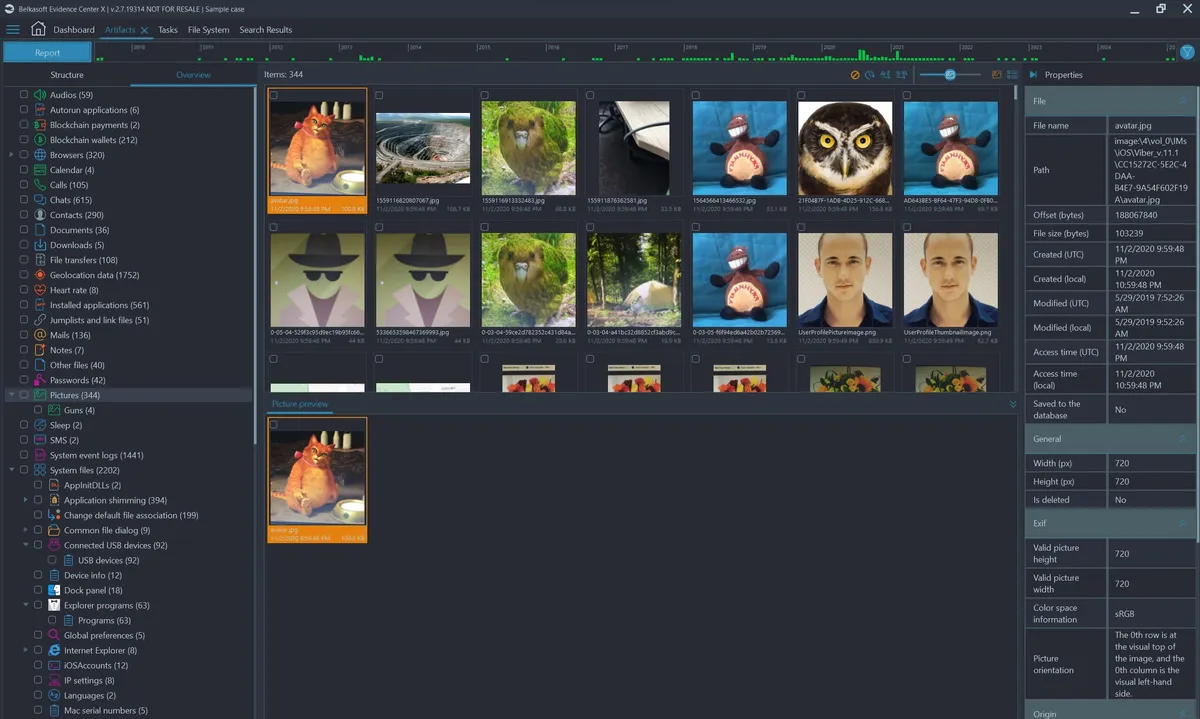
Intelligent search and filtering options
Intuitive graphical timeline
AI-powered information discovery with BelkaGPT
Advanced media file analysis
Forensic data recovery
Workflow automation features
Advanced decryption and access functions
To further assist investigators, Belkasoft X offers special add-on modules for encrypted data and locked mobile devices. These powerful tools enable the recovery of important information that might otherwise remain inaccessible, ensuring a more thorough and comprehensive investigation.
Mobile Passcode Brute-Force Module
Mobile Passcode Brute-Force is an add-on module for Belkasoft X Forensic and Belkasoft X Corporate products. It allows you to bypass security restrictions and crack passcodes on specific iOS and Android devices.
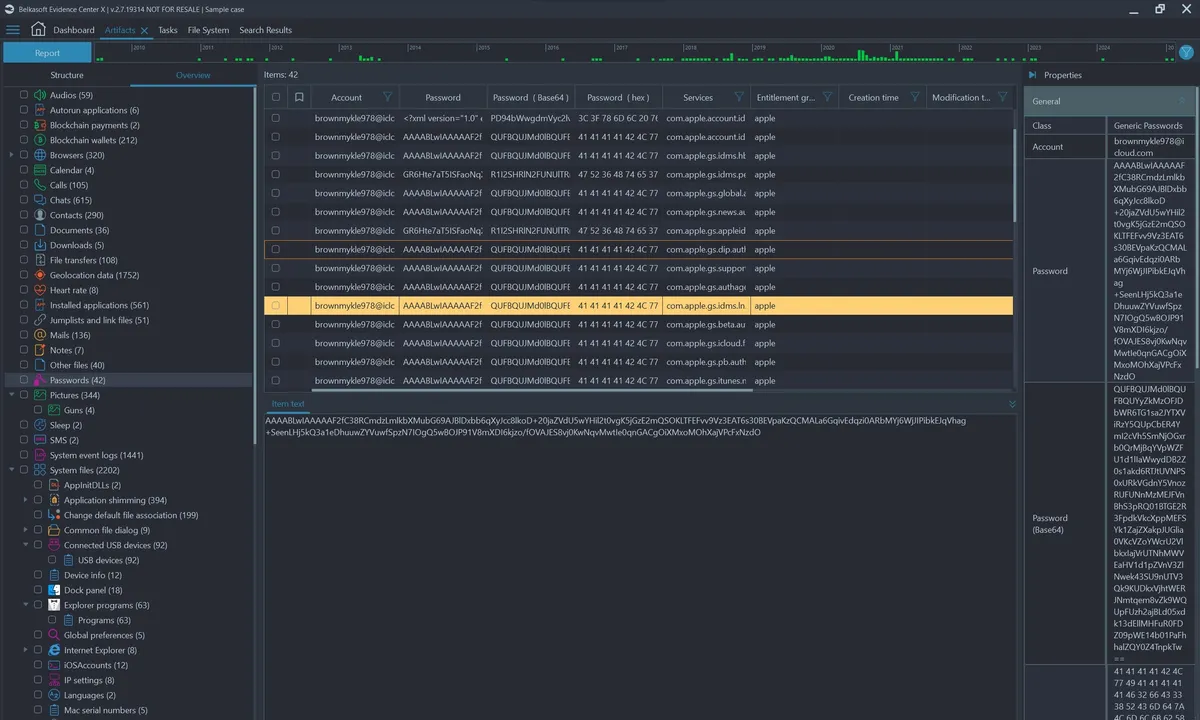
File Decryption Module
The Belkasoft File Decryption Module is an add-on component for Belkasoft X Forensic and Belkasoft X Corporate products. The module brute-forces and decrypts encrypted files found during investigations.
Low-level forensic analysis
Built-in tools for low-level forensic analysis provide convenient navigation of device file systems and examination of raw data.
File System Explorer
Explore all volumes and partitions within the device image, including existing and deleted folders or files, as well as VSS snapshots (Volume Shadow Copies).
PList, Registry, and SQLite viewers
Work more thoroughly with specific types of data to validate your findings and gain additional insights.
Hex viewer
Investigate individual bytes, examine file partitions, convert binary values to different data types, create bookmarks, run custom carving, and apply various encodings.
Select the one that suits you best!
Standard
Simple and cost-effective edition for occasional use
€6,499*
Renewal price: €1,999*
- Belkasoft X Forensic license
- USB dongle included
- Shipping included
- Basic support
No direct purchase: quote after verification of your company or authority.
Email: info@cybersec-check.de
Pro
Scalable solution for investigator teams at government agencies
€7,694*
Renewal price: €2,594*
- Belkasoft X Forensic license
- USB dongle included
- Shipping included
- Basic support
- File Decryption Module included
No direct purchase: quote after verification of your company or authority.
Email: info@cybersec-check.de
Complete
All-in-one solution adjustable to your government's needs
€9,693*
Renewal price: €3,193*
- All Belkasoft X Forensic features
- USB dongle included
- Shipping included
- Basic support
- File Decryption Module included
- Mobile Passcode Brute-Force Module included
No direct purchase: quote after verification of your company or authority.
Email: info@cybersec-check.de
Ultimate
All-in-one solution adjustable to your government's needs
€14,999*
- All Belkasoft X Forensic features
- USB dongle included
- Shipping included
- Basic support
- File Decryption Module included
- Mobile Passcode Brute-Force Module included
- Annual Training Pass
- 3 Years of Support & Maintenance
No direct purchase: quote after verification of your company or authority.
Email: info@cybersec-check.de
BelkaGPT
AI-Powered Forensic Assistant
Enhance your investigations with AI-powered analysis. BelkaGPT helps you discover hidden patterns, generate reports, and accelerate evidence analysis with natural language queries.
- Natural language evidence search
- AI-assisted report generation
- Pattern and anomaly detection
- License Price
- €999*
- Annual Renewal
- €499*
No direct purchase: quote after verification of your company or authority.
Email: info@cybersec-check.de
INFO
Belkasoft X Forensic is only available to government agencies, law enforcement and private experts working for them.
Technical specifications
Belkasoft X Forensic allows data acquisition and analysis from multiple sources
Operating systems:
Windows (all versions, including Windows 11), macOS, Unix-based systems (Linux, FreeBSD, etc.)
Storage devices:
Hard drives and removable media
Disk images:
EnCase, FTK, X-Ways, AFF4, L01/Lx01, DD, SMART, Atola, DAR, DMG, archive files (such as tar, zip and others)
Virtual machines:
VMware, Virtual PC/Hyper-V, VirtualBox, XenServer
Cloud storage:
Amazon S3-based images
Memory:
RAM dumps, hibernation files, page files
File systems:
APFS, BTRFS, FAT, exFAT, NTFS, HFS, HFS+, ext2, ext3, ext4, XFS
Acquisition:
Acquisition to DD or E01 images with optional hash calculation and verification
Operating systems:
iOS (iPhone/iPad), Android, Windows Phone 8/8.1, Blackberry
Data sources:
Mobile backups, GrayKey, UFED and OFB images, UFDR reports, chip-off and JTAG dumps, TWRP images, Blackberry IPD and BBB backups, Android physical and logical dumps, Xiaomi MIUI backups, Huawei HiSuite backups
File systems:
APFS, HFS+, F2FS, YAFFS, YAFFS2, ext2, ext3, ext4
Acquisition:
iOS:
iTunes, agent-based, checkm8-based, lockdown file support, AFC, jailbroken devices support, crash logs, screen capture
Android:
ADB backup, advanced ADB backup, agent backup, rooted devices support, PTP/MTP, EDL for Qualcomm, APK downgrade, agent-based/logical/physical MTK acquisition, Spreadtrum acquisition, automated screen capture, wireless acquisition via an agent on an SD card
SIM cards:
SIM card cloning through a SIM reader device and through native Android functions
Cloud services:
Google (Drive, Sync, Keep, Gmail, Timeline, MyActivity), iCloud, Huawei, Instagram, Microsoft 365, Telegram, VK, WhatsApp
Email:
Yahoo, Hotmail, Opera, Yandex, Mac.com and 25 more webmail clouds
WhatsApp:
backups downloading and QR code-based chat downloading
Supported models:
ArduPilot DIY Drone, DJI Agras MF-1S, DJI Matrice, DJI Mavic, DJI Phantom 3, DJI Phantom 4, DJI Spark, Parrot Anafi, Qysea Fifish P3, Ryze Tello, Sense Fly, Sky Viper, Yuneec H520, Yuneec Typhoon Q500 and other compatible models
Supported artifacts:
Drone geolocation and tracks, operator logs and tracks, pictures, videos
Visualization:
Drone flight route maps and operator route maps in a built-in Maps window
Supported images:
Berla .ivo export for Belkasoft
Supported artifacts:
Geolocation and tracks, chats, SMS messages, and calls, contacts, media, and other information from the infotainment system
Visualization:
Drive routes in a built-in Maps window
Questions about forensic software?
Cybersec-Check
Write to us. We advise you on licenses, setup and training.
Contact us