Belkasoft
Belkasoft is a global leader in digital forensics software, empowering investigators, law enforcement, and cybersecurity teams with advanced tools for evidence recovery and analysis. Through our partnership, we bring cutting-edge forensic capabilities into our digital investigation and security services.
Belkasoft X is an all-in-one tool
It allows you to analyze multiple data sources acquired from different electronic devices within one case.
Computer
Extract data from hard drives, SSDs, and memory dumps with advanced file system analysis.
Mobile Device
Access data from smartphones and tablets including deleted messages and app data.
Cloud
Extract and analyze data from cloud storage services and online accounts.
Car
Recover data from vehicle infotainment systems, navigation history, and connected devices.
Drone
Analyze flight data, images, videos, and logs from various drone models.
Belkasoft X supports every step of your investigation
From unlocking to reporting and sharing.
Unlocking
Brute-force for a range of iOS and Android device models.
Acquisition
Hard drives, mobile devices, RAM, cloud sources.
Analysis
Comprehensive analysis of extracted data.
Physical and logical drive images
Memory dumps
JTAG and chip-off dumps
iOS and Android backups
Mobile file system images
Virtual machines
Drone images
Car images
In addition, Belkasoft X supports image formats created in other tools, like Cellebrite UFED, GrayKey, Magnet Forensics, Exterro FTK (Forensic Toolkit), OpenText EnCase, X-Ways, Oxygen Forensics, Elcomsoft, and Berla.
Reporting
HTML, XML, CSV, PDF, RTF, Excel, Word, EML, KML, RSMF, ProjectVIC JSON, Semantics21, and more.
Sharing
The free Evidence Reader that comes with the tool allows you to create a portable copy of your findings and share them with interested parties in Belkasoft’s user-friendly interface.
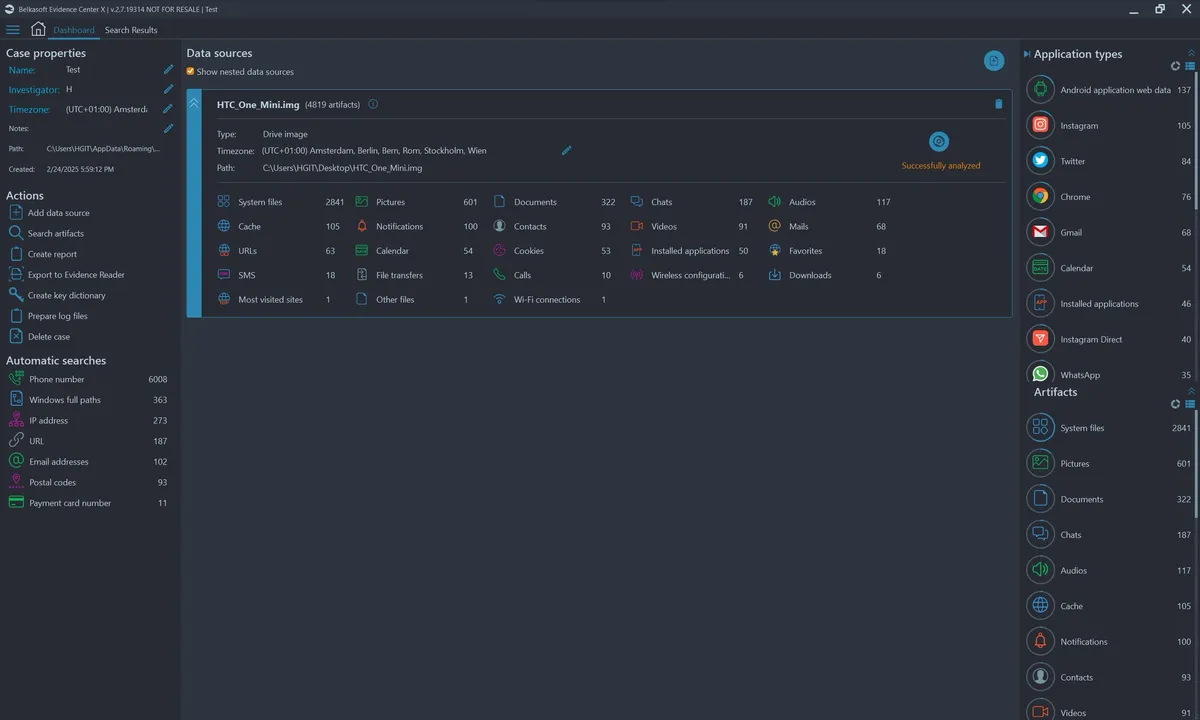
The low-hanging fruit forensics approach
Helps you quickly extract and analyze information from 1500+ artifact types out of the box.
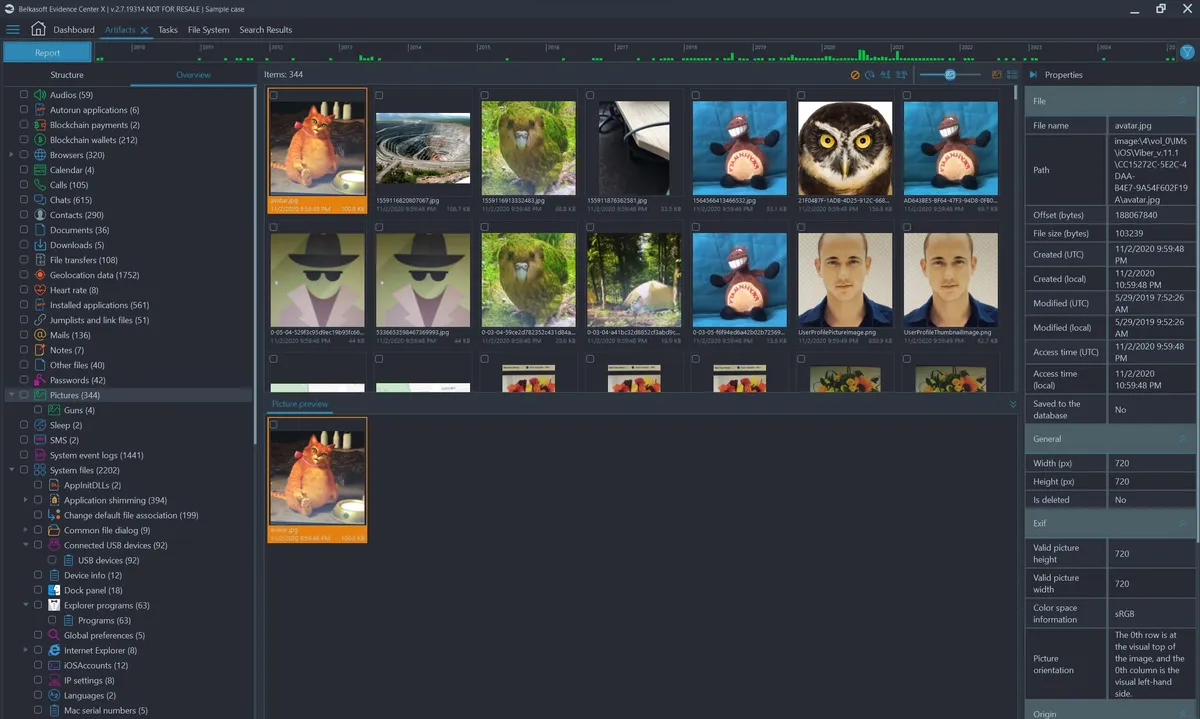
Belkasoft X’s extensive artifact inventory
You do not have to know all data formats, file locations, encryption schemas, or signatures for carving files and individual records.
Built-in tools for low-level forensic analysis
Help you navigate device file systems and examine raw data conveniently.
File System Explorer
View all volumes and partitions inside the device image with existing and deleted folders or files, and VSS snapshots (Volume Shadow Copies).
Hex viewer
Investigate individual bytes, examine file partitions, convert binary values to various data types, create bookmarks, run custom carving, and apply various encodings.
PList, Registry, and SQLite viewers
Work more thoroughly with particular types of data to validate your findings and uncover additional insights.
Belkasoft Triage
Perform effective triage analysis of Windows devices right on the incident scene.
OVERVIEW
Belkasoft T is a free tool designed to assist in situations when an investigator or a first responder is at an incident scene and needs to quickly identify and obtain specific digital evidence stored on a Windows machine. The product is irreplaceable in situations of time pressure, when there is a need to quickly detect the presence of specific data and obtain investigative leads instead of conducting an in-depth analysis of all the digital evidence.
EASY-TO-USE
The product is user-friendly, enabling both experts and non-technical specialists to use it out of the box.
NO INSTALLATION IS REQUIRED
Belkasoft T is portable and can be started from any thumb drive.
QUICK AND SMART
Within minutes you see whether the data you need is there, for example a Skype profile or an Outlook mailbox.
EASY CONFIGURATION
Belkasoft T can be easily configured during operation and does not require special knowledge to set up.
COMPATIBILITY WITH BELKASOFT X
Images acquired with Belkasoft T can be analyzed in Belkasoft X for a deeper insight into the content of the copied data.
NOW FREE!
Unleash the full potential of forensic triage analysis without breaking the bank, ensuring powerful tools are within reach for every investigator.
Features
- Launch Belkasoft Triage from a thumb drive connected to a device being investigated.
- Detect 1500+ types of computer, mobile and cloud artifacts such as emails, chats, browsers, system settings and others.
- Automated acquisition of a computer RAM dump.
- Detect the presence of virtual machines, memory files and mobile backups.
- Detect skin tone in found pictures.
- Calculate file hash values and show an immediate alert on files with known hashes.
- Stop the analysis at any time once you have enough information.
- Export discovered results partially or entirely.
- Select evidence to be included into the resulting image.
How it works
How to use Belkasoft Triage in five steps
Run Belkasoft T from a thumb drive.
Select a folder or disk. Acquire RAM if needed.
Configure options, such as hash set databases and skin detection.
Start the analysis and review the discovered application profiles.
Export selected data into an image readable by Belkasoft X as well as other forensic tools.
Belkasoft RAM Capturer
Belkasoft Live RAM Capturer is a free forensic tool that extracts complete computer memory contents despite anti-debugging protections and is compatible with Windows.
Why Memory Dump Is the First Thing To Do During the Acquisition
Memory dumps are a valuable source of ephemeral evidence and volatile information. They can contain passwords to encrypted volumes like:
- TrueCrypt
- BitLocker
- PGP Disk
As well as account login credentials for various webmail and social network services, including:
- Gmail
- Yahoo Mail
- Outlook.com
- X (Twitter)
Additionally, they can contain file sharing credentials for services like:
- Dropbox
- Flickr
- OneDrive
To extract ephemeral evidence from already captured memory dumps, forensic experts must use specialized analysis software like Belkasoft X. Some other tools can also be employed to extract passwords from encrypted volumes.
Designed to Bypass Active Anti-Debugging and Anti-Dumping Protection
Acquiring volatile memory from a computer running a debugging protection or anti-dumping system is a challenging task. Most memory acquisition tools operate in the system’s user mode, rendering them unable to bypass the defense mechanisms employed by these protection systems, which function in the system’s most privileged kernel mode.
Belkasoft Live RAM Capturer is designed to function effectively even when an aggressive anti-debugging or anti-memory dumping system is in operation. By operating in kernel mode, Belkasoft Live RAM Capturer operates on the same level as these protection systems, enabling it to accurately capture the address space of applications protected by the most sophisticated systems, including nProtect GameGuard.
Creates Forensically Sound Memory Dumps
Belkasoft Live RAM Capturer boasts the smallest footprint possible, eliminating the need for installation. It can be launched in mere seconds from a USB flash drive. Unlike many competing tools that operate in system’s user mode, Belkasoft Live RAM Capturer is equipped with 32-bit and 64-bit kernel drivers, enabling it to function in the most privileged kernel mode. Memory dumps obtained with Belkasoft Live RAM Capturer can subsequently be analyzed using Belkasoft X.
Compared to Other Volatile Memory Capturing Tools
Belkasoft Live RAM Capturer outperforms competitors due to its design, operating in kernel mode and avoiding anti-dumping activities.
Belkasoft Live RAM Capturer outperformed competing tools in acquiring protected memory images.
Tools tested (Belkasoft's original test):
- AccessData FTK Imager 3.0.0.1443
- PMDump 1.2
- Belkasoft Live RAM Capturer 1.0
The results:
- AccessData FTK Imager 3.0.0.1443 contained all zeroes in place of actual data for the protected memory set.
- PMDump 1.2 returned random data.
- Belkasoft Live RAM Capturer 1.0 correctly acquired the protected memory set.
Belkasoft launched Karos, a computer game protected with nProtect GameGuard, and conducted an active chat session. They then attempted to obtain the entire memory dump of the system using all three memory dumping tools. Finally, they analyzed the memory set belonging to the protected game.
Consequences of Using a Wrong Tool
Using an inappropriate tool to capture memory from applications with anti-dumping protection (like online games or malware) can lead to problems. At best, the tool might retrieve empty or random data instead of the actual memory content. At worst, the protection system could detect the attempt, destroy the targeted information, and even cause a system crash (kernel mode failure), preventing any further analysis. This often happens when a user-mode memory dumping tool is used against kernel-mode protection systems.
Compatibility and System Requirements
Belkasoft Live RAM Capturer is compatible with 32-bit and 64-bit editions of Windows including XP, Vista, Windows 7/8/10/11, 2003 and 2008 Server. The tool does not require installation, and can be launched in seconds from a USB thumb drive.
Why Our Partnership Matters
Empowering Investigations Through Forensic Innovation
Together with Belkasoft, we bring next-generation digital forensics and incident response capabilities to our clients. From deep-dive investigations to enterprise-grade data acquisition, our collaboration enhances every stage of the investigative process.
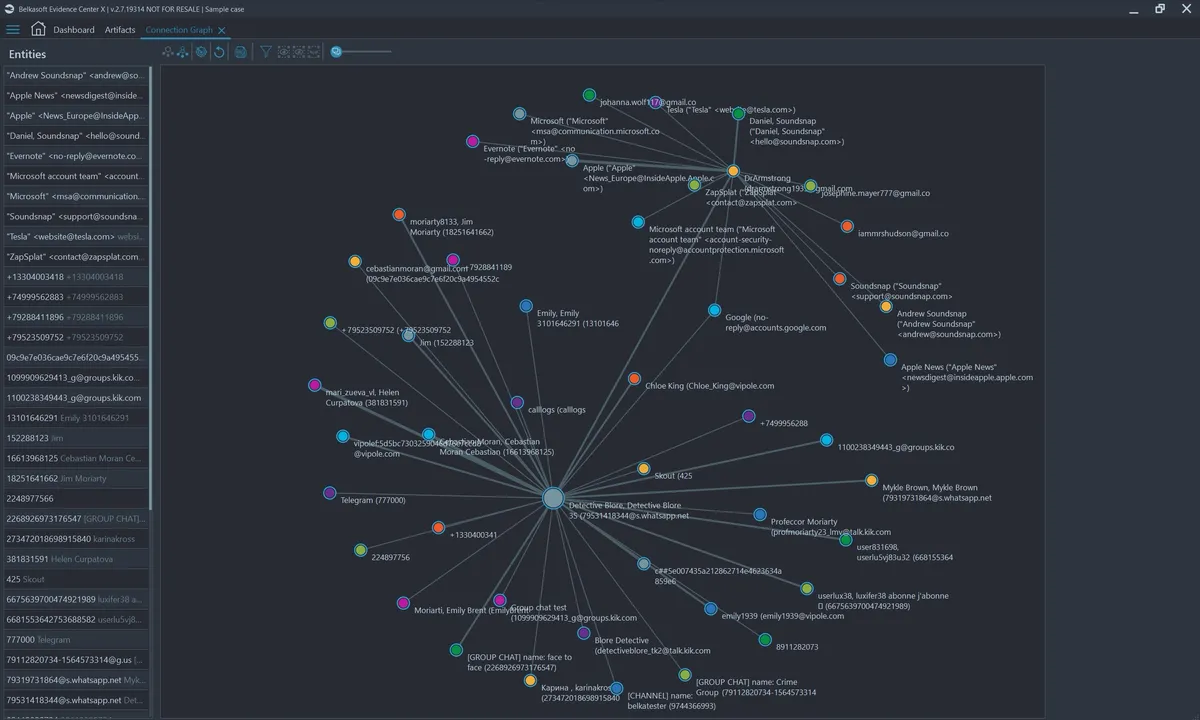
Belkasoft X Forensic
A comprehensive digital forensics suite that supports every step of your investigation, from acquisition and in-depth analysis to building reports and sharing evidence.
Learn more about Belkasoft X ForensicBelkasoft X Corporate
A smart digital forensics solution for corporate security, cyber incident investigations, and eDiscovery. Acquire data from local and remote devices, analyze, and export findings to industry-standard formats.
Learn more about Belkasoft X CorporateQuestions about forensic software?
Cybersec-Check
Write to us. We advise you on licenses, setup and training.
Contact us